The world doesn’t pause. Neither does our security. Optilogic models your most sensitive supply chain information: costs, suppliers, footprints, and strategic scenarios. We protect it with controls that are independently audited, continuously monitored, and always on.



Every supply chain decision carries risk. Understanding that risk requires data you can rely on. Knowing your data is protected and secured allows you to take calculated risks with confidence and move your business forward.
Technology keeps changing. What doesn’t: the security standards we hold our platform to. Our program rests on three pillars:

External and independent auditors check our controls.

Role-based access controls, encryption, 24/7 monitoring, and proactive mitigation work together, so no single failure exposes your data.
People and systems get access to the minimum of what their role requires.

Always on. Independently verified.

Controls independently audited
Level 2 compliance underway
Independent testing of the product and network annually.
Customer data encrypted at rest and in transit (TLS 1.2+)
Required for all Optilogic staff access to cloud products and internal systems
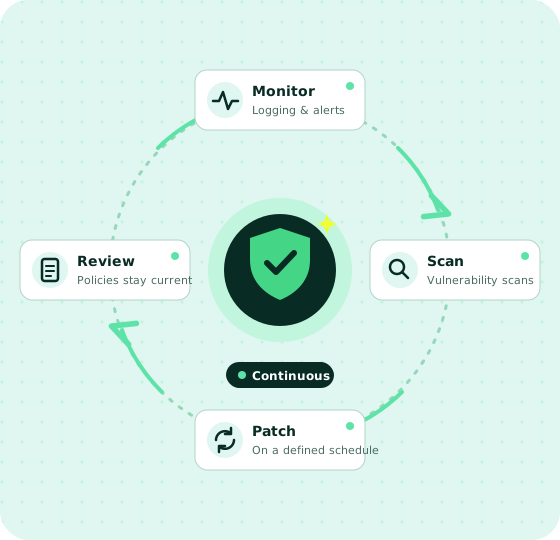
An always-on model runs with constantly refreshed data, so protection has to be proactive and constantly managed too. Security here is a continuous practice, not an annual event. A 24/7 Security Operations Center manages logging and monitoring. Vulnerability scans and patching follow a defined schedule and are embedded in our engineering pipelines. We review our security policies as the threat landscape shifts, drawing on continuous updates from industry experts and cybersecurity partners.

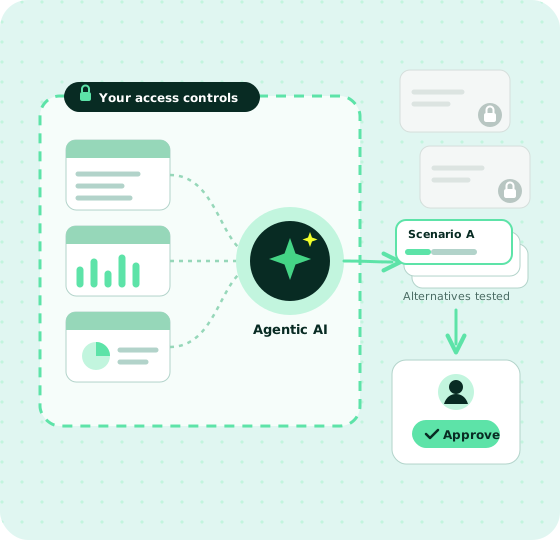
Agentic AI senses what’s changing, models what’s next, and recommends what to do about it. Our AI informs decisions that matter; it runs inside the same protections as the rest of the platform.
Connected AI follows your permissions. When you connect your AI tool to Optilogic’s AI via MCP, it works within the access your administrators have granted. Your AI tool remains a third-party service, governed by your agreement with its provider.

An independent auditor tests our controls against the Security Trust Services Criteria across a full observation period each year. Our current report and bridge letter are available in the Trust Center. We plan to add Availability and Confidentiality in 2027.
We meet the U.S. Department of Defense’s Cybersecurity Maturity Model Certification (CMMC) Level 1 requirements. We’re now implementing the NIST SP 800-171 controls required for Level 2.
Independent security firms test our product and network annually. Reports are available to customers and prospects under NDA.
Named security owners, defined roles, and a formal risk management function mean someone is responsible for every control.
Customer data is encrypted at rest and in transit, and company laptops and workstations use full-disk encryption.
Access follows least-privilege principles. All Optilogic staff access to our cloud products and internal systems requires multi-factor authentication. Audit logging records are continuously monitored by a Security Operations Center. Customers can sign in with single sign-on through OpenID Connect (OIDC), so your identity provider’s MFA and access policies apply. We also use OAuth 2.0 to secure access to your data and models.
Your data belongs to you. Each customer’s data lives in its own per-tenant database, isolated from other customers. Optilogic’s Data Protection Policy outlines the right to erasure for individuals and details approved destruction methods for various data types.
Our standard deployment runs on Microsoft Azure across multiple US regions, in facilities with strong physical and environmental security.
Customer data is backed up under a formal backup policy. We test our disaster recovery plan annually and document the results.
We build security in from the start. A defined Software Development Lifecycle (SDLC), formal change management policy, and vulnerability and patch management are built into our development pipeline.
Formal policies cover monitoring, detection, containment, and remediation. We maintain a business continuity plan, test our disaster recovery, and document the outcomes. Breach notification procedures are defined in advance.

Every employee completes security awareness training annually. Company devices run endpoint detection and response, anti-malware protection, and secure patching, and asset management policies keep every device and system accounted for and monitored.
We have a designated Data Privacy Officer, a documented breach notification policy and process, and Data Protection Impact Assessments.
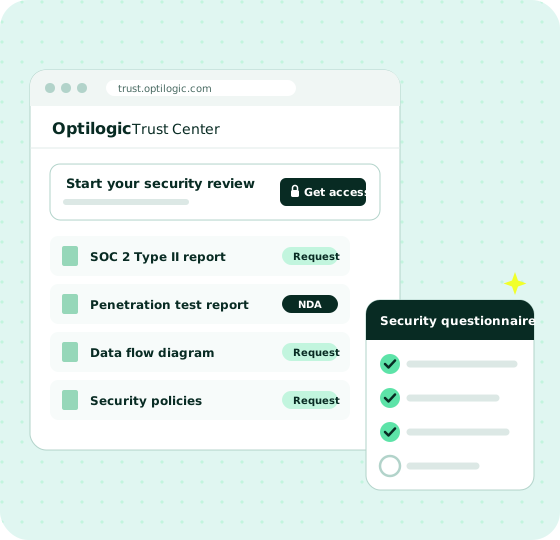
Our Trust Center gives your security and procurement teams what they need, and our team of security experts works through your review as true partners. Documents include:
Most documents are available on request, and sensitive ones under NDA.
Report a security concern: support@optilogic.com
Let’s make sure your security review doesn’t slow it down.
This page describes Optilogic’s current security practices and does not create contractual commitments. Binding terms are in your agreement with Optilogic.